The AI versus AI era of cybersecurity
As AI continues to be used by threat actors, Horizon3’s Keith Poyser discusses the new era of cybersecurity, and why human-in-the-loop is no longer viable
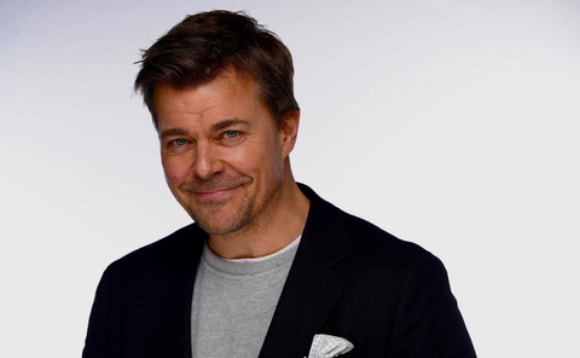
“This is an AI versus AI era in terms of cyber attackers and defenders,” declares Keith Posyer, VP EMEA, Horizon3.
“[Cybersecurity] has got to be autonomous without human-in-the-loop to keep up pace.”
Horizon3 provides automated, continuous penetration testing and exposure management that allows organisations to test their environments from an attacker's perspective.
For years, cybersecurity strategies have centred on identifying vulnerabilities and responding to threats as they emerge.
However, AI is changing the speed at which attacks unfold and is creating a new battleground.
Organisations are grappling with what one executive described as a “tsunami” of vulnerabilities.
According to IBM’s X-Force Threat Intelligence Index 2026, “AI is reshaping attacker operations by compressing decision cycles and enabling faster experimentation during active intrusions.
“Adversaries increasingly use AI to accelerate research, analyse large data sets and iterate on attack paths in real time, allowing them to adjust tactics as conditions change rather than relying on static, preplanned actions.”
Speed is now of the essence, and relying on a human versus AI approach in cybersecurity will create vulnerabilities for organisations in the future.
Why speed is key in cybersecurity
As an autonomous hacking platform, Horizon3 is able to step into the shoes of an attacker and see how fast it actually takes for compromises to occur.
Poyser explained that Horizon3’s average time to domain compromise in a client is 13 minutes, highlighting how quickly attackers can move through an environment once an initial foothold is gained.
AI is minimising the time between threat actors discovering a vulnerability and exploiting it, while allowing attackers to automate attacks.
Humans are unable to keep this pace.
The speed of humans is no longer enough
“The era of human-led or human in the loop is just impractical,” Poyser says.
“If you look at the sheer volume of attacks, exploits, and vulnerabilities being discovered, if a human is involved in even five per cent of the gating decisions in a semi-autonomous pen test, it's not possible. They just can’t keep up.”
Poyser recalled a scenario where Horizon3 followed a human penetration testing team into an organisation with approximately 5,000 assets.
While human testers had already completed their assessment, the autonomous platform was able to identify a route that allowed it to bypass EDR controls, escalate privileges and ultimately gain access.
The test illustrated the limitations of relying solely on human-led testing, especially when organisations are facing up against AI cyber criminals.
“The human is typically testing five per cent of the attack surface,” he explains.
“We’re looking for the needle in the haystack that attackers are going to find.
“The only way you can do that is at speed and autonomously.”
The challenge for security teams is not only the speed of attacks, but the sheer volume of vulnerabilities they are required to manage.
According to Poyser, many organisations are overwhelmed by vulnerability data and struggling to determine which issues pose a genuine threat.
Rather than attempting to address every weakness, he argues that security leaders should focus on understanding which vulnerabilities can actually be exploited.
“We don’t really care about vulnerabilities; we care about exploitability in your environment.”
The shift from vulnerability management to exploitability is a key reason why autonomous security is becoming increasingly important.
Poyser believes organisations increasingly need autonomous security capabilities to keep pace with AI-driven threats.
“I think the autonomous AI versus AI message is really, really important,” he stresses.
The industry is beginning to move towards offensive cybersecurity, allowing AI to fight AI when it comes to keeping organisations secure.
Regulations have played a large role in this shift.
“The market has moved towards offensive cyber.
“We’re seeing requirements under DORA, ECB guidance, NIS2, and this requirement to continuously test your attack surface, so the market has caught up a little bit.”
As the number of AI tools increases, organisations are facing a separate challenge: deciding which security solutions can actually deliver on their promises.
Building trust in cybersecurity
With so many cybersecurity solutions available on the market, end-users want to ensure tools provide value.
Poyser explains, “Customers are more interested in buying outcomes. They’re not necessarily interested in buying more tooling.”
“I think cyber at times has been its own worst enemy in terms of FUD (fear, uncertainty and doubt).
“There’s been a little bit of a trust issue in cyber in terms of commitment/delivery from some vendors in the market, so trust has eroded,” Poyser explains.
While cyber remains an innovative space, trust and promises to deliver need to come to fruition.
“If [vendor tools] are not stopping the attacker, there's a question about trust and performance.
“The attacker’s perspective is the only real way you can trust your environment and its defensibility and effectiveness against attacks.”
For Poyser, the debate comes down to speed.
“The fastest we breached a large financial institution was 77 seconds,” he says.
“What we’re saying is, if your SOC and your security team and tooling can’t respond in 76 seconds or less, then you’ve lost.”